Tag: microblogimport20260616
-
Platform engineering is what makes AI enterprise-ready
As we’ve found, writing AI-powered software is the easy part. Testing it, securing it, operating it at enterprise scale – that’s where things get interesting. “Guardrails,” all that. Purnima lays this out: a shift from deterministic systems (input goes in, predictable output comes out) to probabilistic ones where agents wander around exploring multiple paths to…
-
de-weirding enterprise AI
Ethan Mollick: The de-weirding impulse produces a second, deeper failure: it leads companies to default towards automation rather than augmentation. When leaders see studies showing productivity gains of 30% from AI, their instinct is to cut 30% of the workforce. That arithmetic is simple. What is hard, and requires genuine imagination, is asking a different…
-

The New Bottleneck That Will Chill Your AI Vibes
Platforms are helpful, from 2025 DORA Report. Getting software from idea to production quickly has always been important, but the increase in AI-driven application deploys is about to overwhelm even the best laid golden path to production. We can feel in our bones developers are already revving apps more frequently. The 2025 DORA Report found…
-

Check out the live reacording of this week’s Software Defined Talk. Final episode posted tomorrow, on Friday if you prefer traditional podcast.
-
Histoires Prodigieuses, Forward Deployed Vibes, and Skyrgamur – Related to your interests, Wednesday
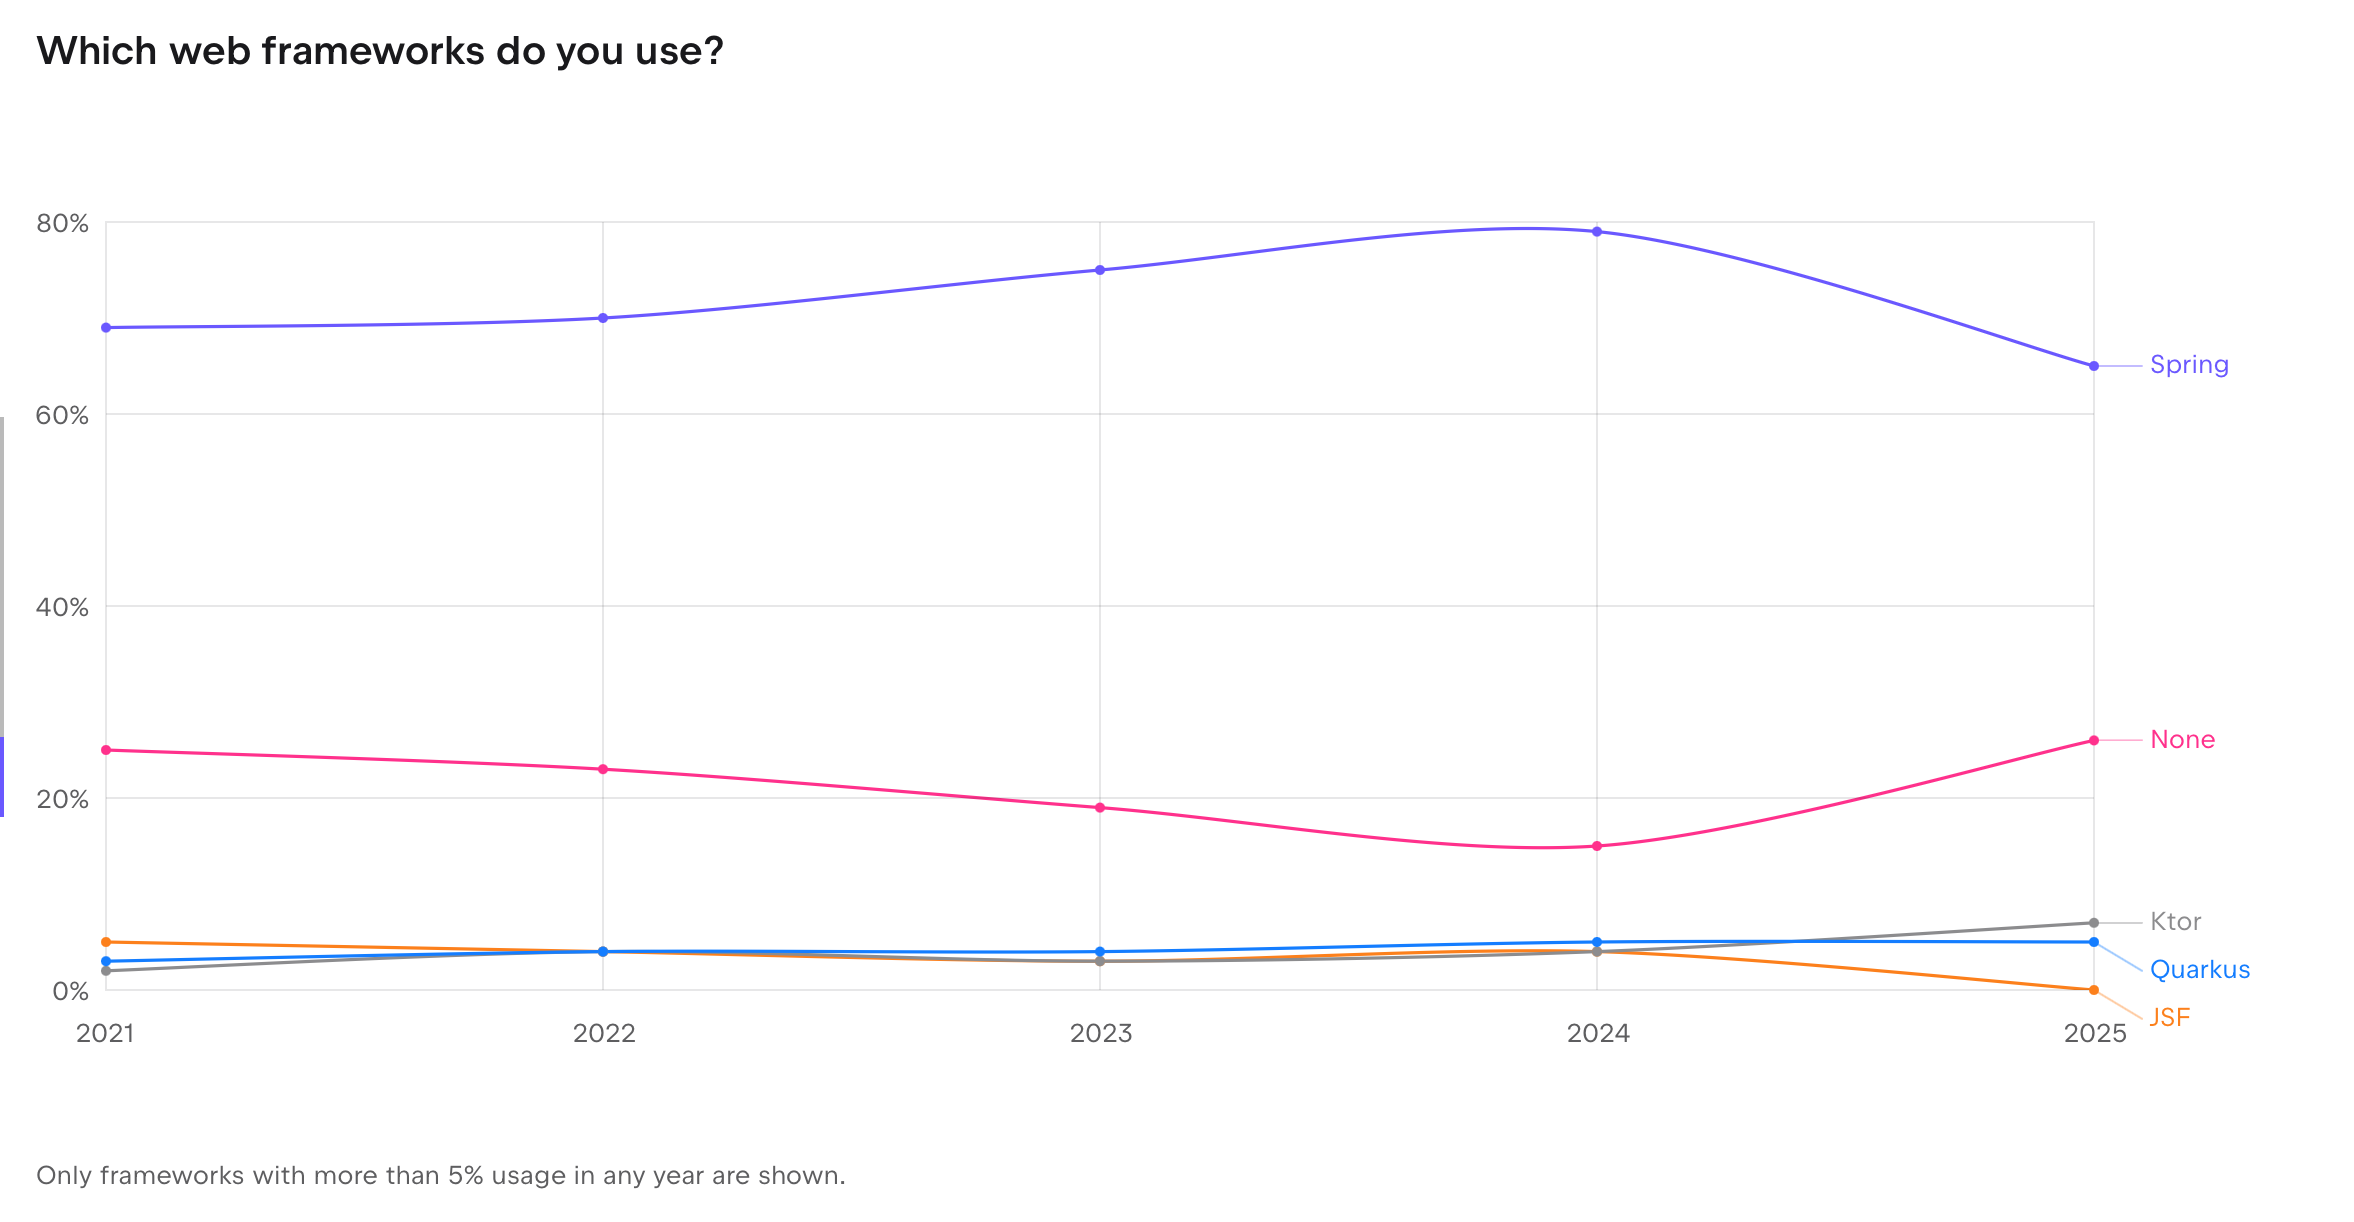
Also: Spring still number one, KubeCon AI workloads, the end of Doctor No, and a buyer’s market for employees. Spring still king, from The State of Java 2025, JetBrains. Related to your interests 🤖 From Red Hat OpenShift to VMware Cloud Foundation 9: A Journey to a Unified Cloud Operating Model – A defense-industry case…
-

Five Disneys, Conviction Collapse, and sk8erboi2006 – Related to your interests, Tuesday
Also: local models worth running, Susan Sontag on list-making, GraalVM as thriller novel, and the slow ROI of children. The Prodigal Daughter (1903), John Collier. Via New Cartographies. Related to your interests Recommended local models – “I’ve experimented with the following models and have found useful applications (mostly around chat, MCP and coding) with all…
-
Using HATEOAS for agentic AI – a demo
My co-worker Adib did a video showing how to use Spring HATEOAS to make existing REST APIs agent-friendly. Instead of wrapping your 700 APIs as MCP servers and dumping all those tool definitions into the context window, you build a an adapter layer that lets agents discover what they can do by following links in…
-

Hot modems, dinergoths, the platform bottleneck, and the SaaSpocalypse – Related to your interests, Monday
Also: sovereignty’s control plane, 81,000 people tell Anthropic what they want, Google sells its fiber, and oats for the sparrows, and cake Related to your interests My pal Adib Saikali wrote up an MCP security guide covering how to think about securing MCP servers in the enterprise (no lead-generation required, just a straight-up PDF download).…
-
Securing AI
More “how do we secure this AI stuff” talk with David Zendzian on today’s live stream. He’s recently gone Claude Crazy so I wanted to get his CISO-supremo talk on thinking through the risk management for AI in enterprises. Each time I tried to come up with a problem, he was good finding the fix.…
-
If you’re wondering how cold fusion produces pollution, let alone a lot of it, don’t worry, this is explained in a chapter by one teenaged prodigy tennis player to another, wherein the latter is wearing a blindfold to improve his other senses but can’t find a bathroom, so he asks the other player for help,…
-
MCP Security Guide
My pal Adib Saikali wrote up an MCP security guide covering how to think about securing MCP servers in the enterprise (no lead-generation required, just a straight-up PDF download). It gets into access tiers (open, group, and user-level servers), authentication with OAuth 2.1, identity propagation models (when to use service accounts vs. forwarding user identity),…
-
KubeCon EU 2026, bottlenecks, Corporate Bullshit Receptivity, and the End of the Meat-Mouse – Related to your interests, Wednesday
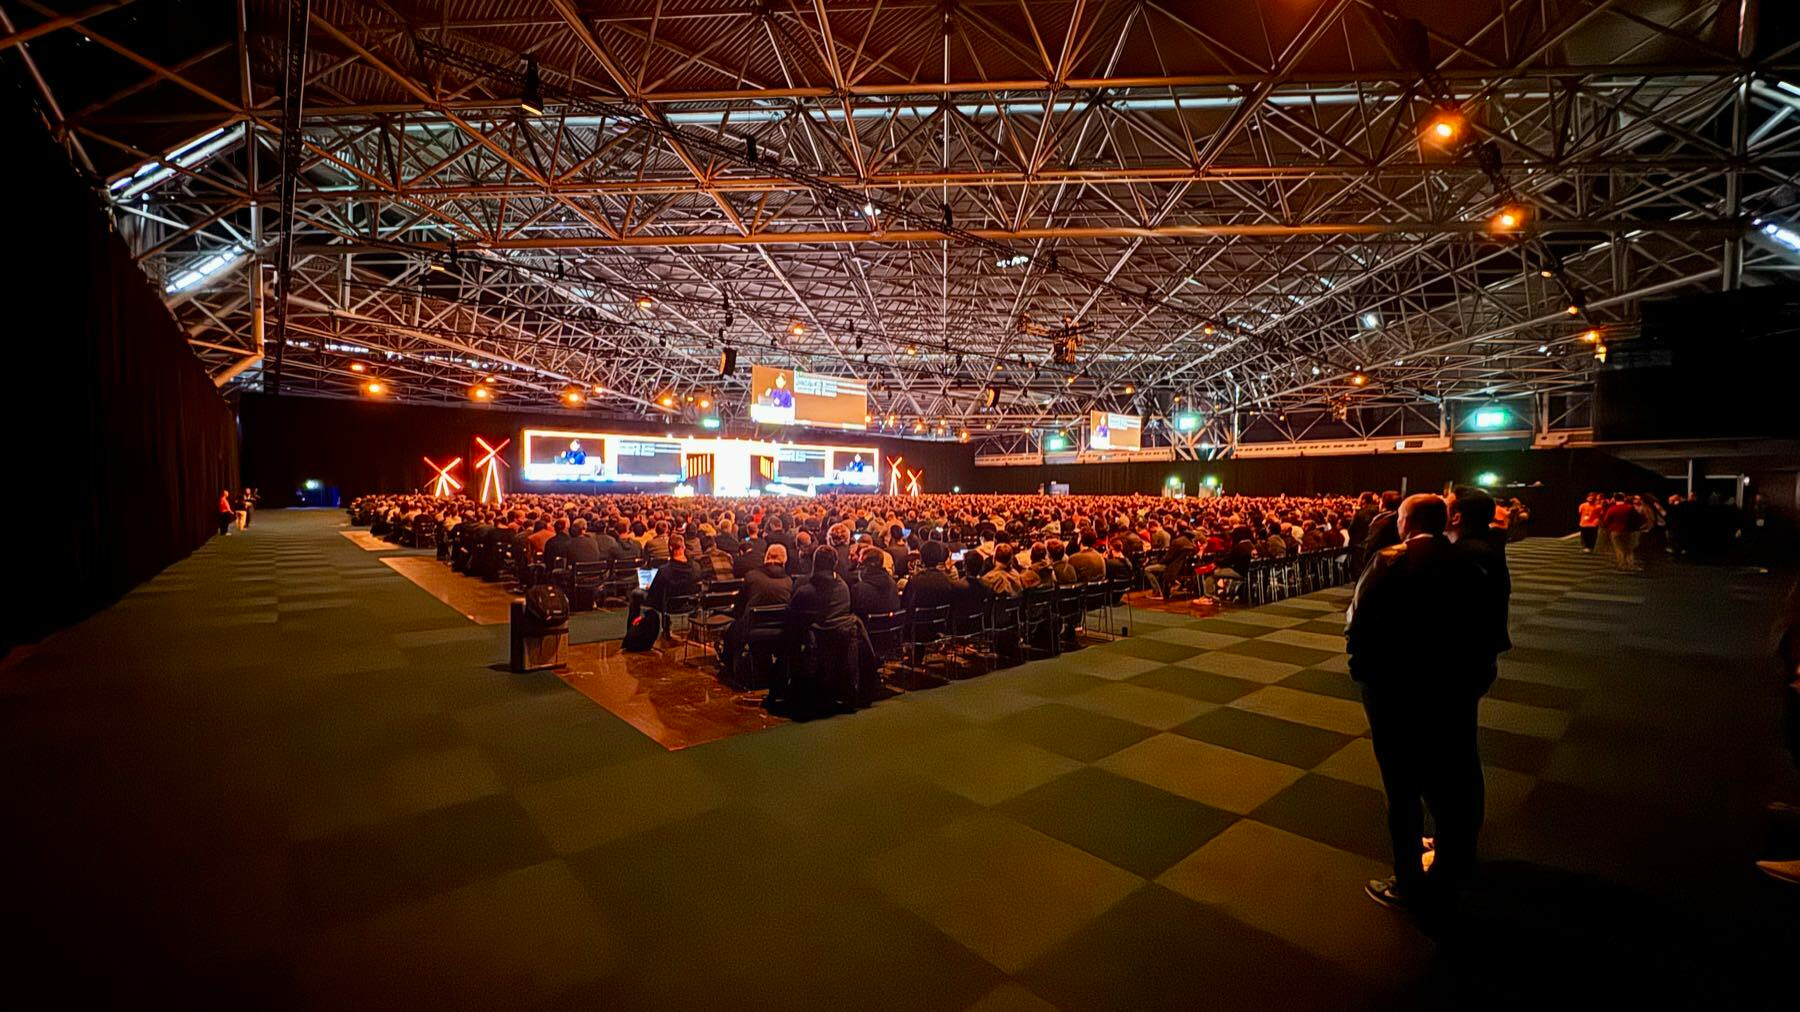
Also: sovereign AI, Claude Code auto mode, FCC bans foreign routers, Walmart digital price tags KubeCon EU 2026 KubeCon is crazy big. James says something like 13,500+ people. They’re going for another infrastructure grab: all the stuff used to run AI. It’s worth asking who they’re competing with there. I have no idea how OpenAI…
-

Kubernetes is the bottleneck, and you can get through it with a platform
Photo by Daniel Bryant. Another great KubeCon talk from Abby Bangser imploring the Kubernetes people to remember how important platforms are: they make all of his stuff usable for developers and valuable to the organizations that run it all. Without a platform, you’re just put another bottleneck in place. Also, see the go she started,…
-
VMware/Broadcom at KubeCon EU 2026
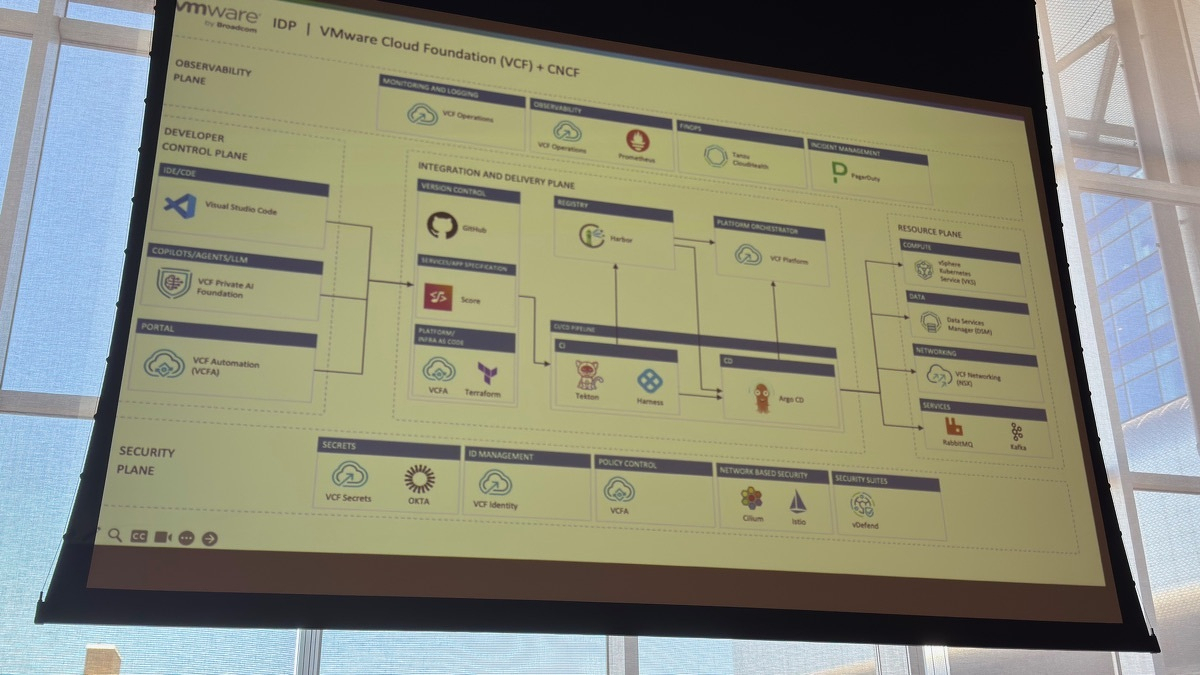
Here’s Claude’s take on VMware’s stuff at KubeCon – just some light editing for me. KubeCon + CloudNativeCon Europe 2026 ran March 23-26 in Amsterdam. Here’s what VMware by Broadcom announced. VKS 3.6 Ships The VKS stack as seen at VMUG Connect Amsterdam 2026. VMware vSphere Kubernetes Service 3.6 shipped with Kubernetes 1.35 support, RHEL…
-
The end of the meat-mouse
The agency in agentic AI feels a lot more like giving the users – the humans – agency they didn’t have. That’s what’s making it useful for me, from sorting out dumb-shit home-networking incompatibilities, figuring out taxes, and otherwise sorting my shit out. When you unleash something like Claude code on all the messy and…
-

The Mythical Agent-Month, Retirement Cartoons, and Coffee Brains – Related to your interests, Monday
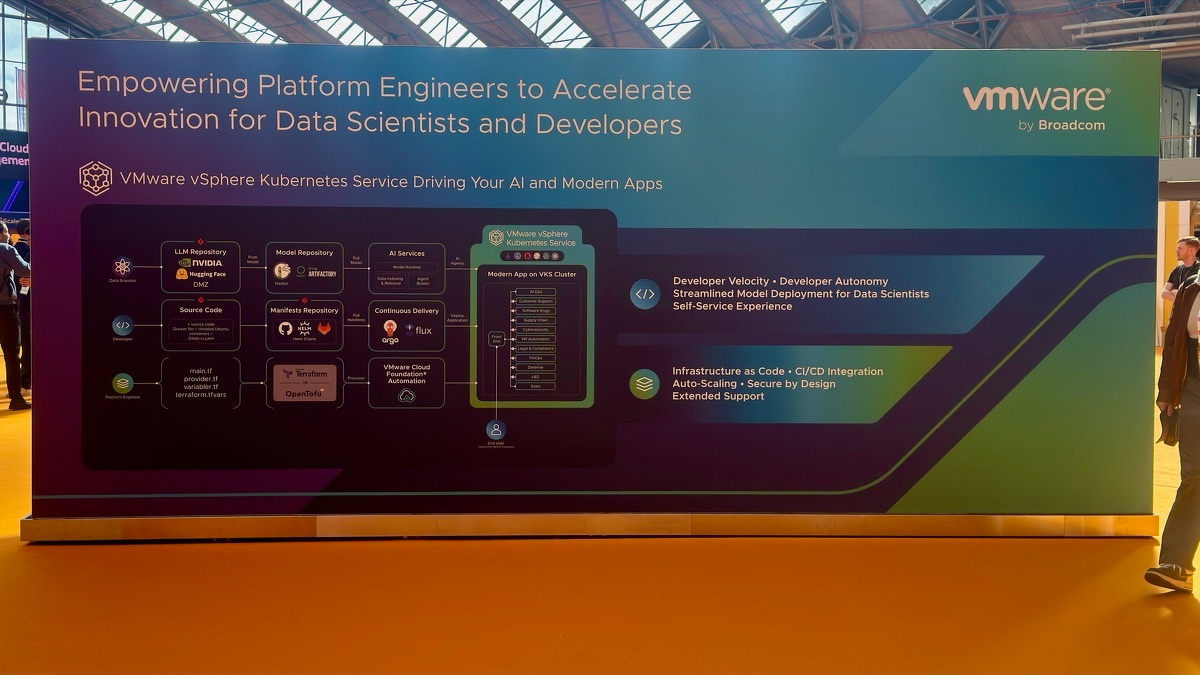
Spotted in the Tenerife South Airport, February, 2026. Related to your interests Broadcom Empowers Platform Engineers to Accelerate AI and Modern Application Innovation on Kubernetes – Round-up of VMware Kubernetes releases and announcements at KubeConEU 2026. Strengthening the Cloud-Native Ecosystem Through Upstream Collaboration – VMware’s open source work in the kubernetes community. Broadcom expands Kubernetes…
-
Using AI to help with SRE, ops, etc.: The problem, he said, is that Claude “will get wrong correlation versus causation.” It’s like a new joiner on the team, they will think “oh, it’s a capacity problem, when actually you lost your cache.” “This is why we can’t trust LLMs for incident response,” said Palcuie.…


You must be logged in to post a comment.